Invited Speaker
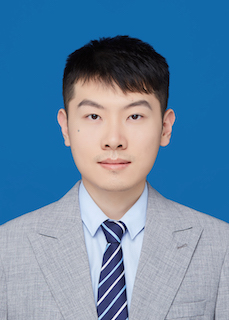
Wei Zhou
Associate Professor, School of Cyber Science and Engineering, Huazhong University of Science and Technology, ChinaSpeech Title: Are We There Yet? Real-World IoT Firmware Emulation and Security Testing in the LLM Era
Abstract: As IoT devices become increasingly integrated into critical infrastructure, scalable and effective firmware security testing has never been more important. Yet, despite a decade of research and rapid advances in large language models (LLMs), how far are we from reliably emulating and testing real-world IoT firmware at scale? In this talk, we systematically revisit over 20 representative firmware emulation and fuzzing techniques developed over the past decade, examining their fundamental challenges, technical advances, and limitations. Moving beyond small, curated benchmarks, we further conduct a large-scale evaluation using over 4,000 real-world black-box firmware samples across an end-to-end security analysis pipeline.Our findings reveal a striking reality: only 1,580 firmware samples (34%) can be successfully fuzzed by at least one existing tool, with an average code coverage of approximately 10% and frequent false crashes and hangs. By uncovering the root causes of these limitations, this talk highlights the critical gaps in today's techniques and explores future opportunities for scalable, intelligent, and LLM-assisted firmware security analysis.
Biography: Wei Zhou is an Associate Professor at the School of Cyber Science and Engineering, Huazhong University of Science and Technology. His research focuses on systems security, particularly IoT firmware vulnerability detection and analysis. He has discovered vulnerabilities affecting over 100 million IoT devices and received official acknowledgments from major companies, including Amazon, JD.com, and Xiaomi. He has published more than ten papers in leading security conferences and journals, including IEEE S&P, USENIX Security, NDSS, ACM CCS, and IEEE TIFS.